Generative AI Use Policy: What Every Company Needs
Learn why a Generative AI Use Policy is essential for structured companies to prevent data leaks, ensure compliance, and boost operational safety.
- Generative AI Use Policy
- Enterprise AI Governance
- Data Security
- Process Automation
- AI Compliance
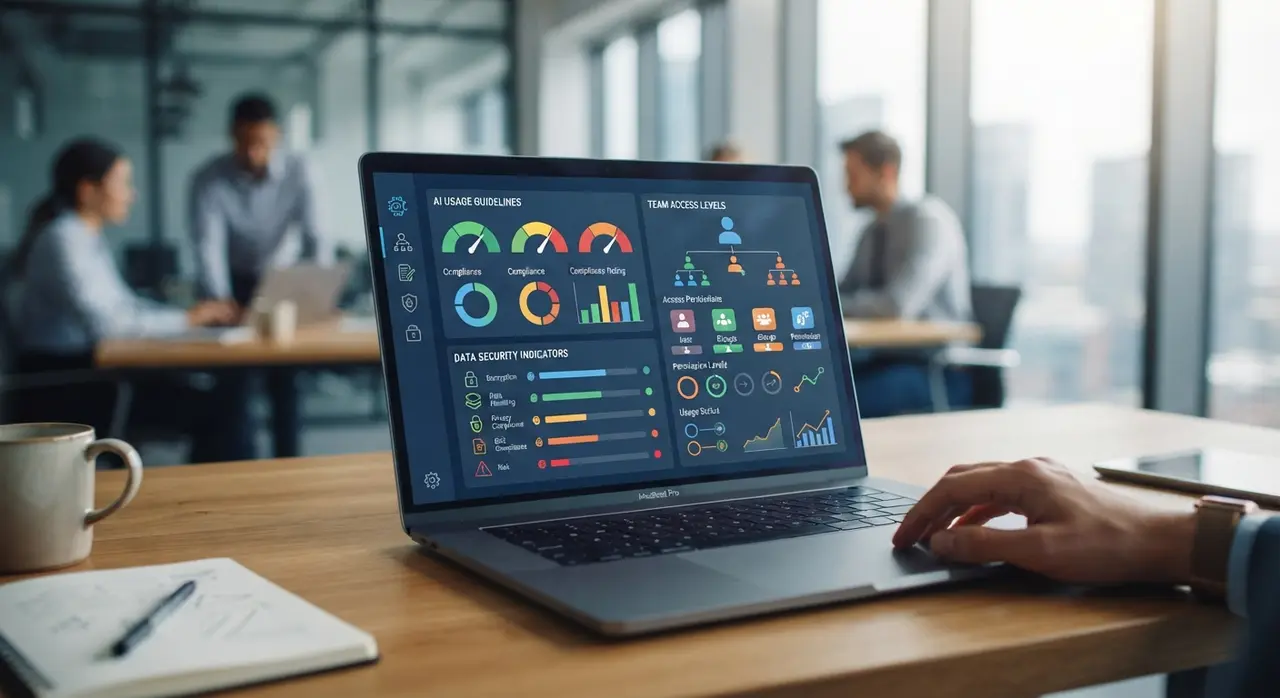
A Generative AI Use Policy is a formal enterprise document that establishes operational guidelines, security guardrails, and compliance standards for workplace artificial intelligence adoption. Implementing a clear policy ensures that every structured company should have explicit boundaries to protect confidential IP while empowering teams to automate daily tasks safely.
Shadow AI Creates Unseen Operational and Legal Vulnerabilities
Uncontrolled employee adoption of public AI tools exposes organizations to severe legal and data privacy risks. When employees paste proprietary code, financial forecasts, or customer records into consumer-facing generative models, that data can be retained for model training without enterprise consent.
Without formal rules, organizations face three primary operational hazards:
- Data Leakage: Sensitive corporate information entering public language models.
- Hallucination Risks: Unverified AI-generated figures or contracts reaching clients without quality control.
- Copyright Infringement: Inadvertent use of protected material in external deliverables.
Adopting agentic AI systems without corporate guardrails creates chaos across operations, finance, and support teams. Establishing clear usage rules is the first line of defense against operational erosion.
Core Pillars of an Effective Enterprise Generative AI Policy
A comprehensive AI policy balances risk mitigation with operational agility by defining clear usage categories. Rather than imposing a blanket ban that paralyzes innovation, a well-crafted document that every company builds must define which tools are permitted and under what parameters.
To ensure total clarity across all business departments, your policy charter should explicitly define five main components:
- Approved vs. Prohibited Tools: Clear listing of enterprise-sanctioned platforms versus consumer tools.
- Data Classification Standards: Specific guidelines detailing what data categories may interact with AI engines.
- Approved Use Cases: Standard operating procedures for draft generation, code inspection, and data analysis.
- Human-in-the-Loop Requirements: Mandated human validation steps for all customer-facing or decision-critical outputs.
- Enforcement & Consequences: Transparent operational protocols for handling policy non-compliance.
The table below outlines a standard framework for classifying data interactions with generative systems:
| Data Sensitivity Level | Permitted AI Environment | Human Review Required? | Example Use Cases |
|---|---|---|---|
| Public Data | Public & Enterprise Tools | Optional | Summarizing market reports, drafting generic social copy |
| Internal Non-Sensitive | Enterprise Shared Tools | Recommended | Formatting meeting notes, structuring internal slide outlines |
| Confidential / PII | Isolated Private Models Only | Mandatory | Processing customer inquiries, analyzing vendor invoices |
| Restricted / IP | Strictly Prohibited on External AI | Mandatory Legal Review | Core trade secrets, unreleased financial audits, legal strategy |
Human-in-the-Loop Governance: Balancing Autonomy with Oversight
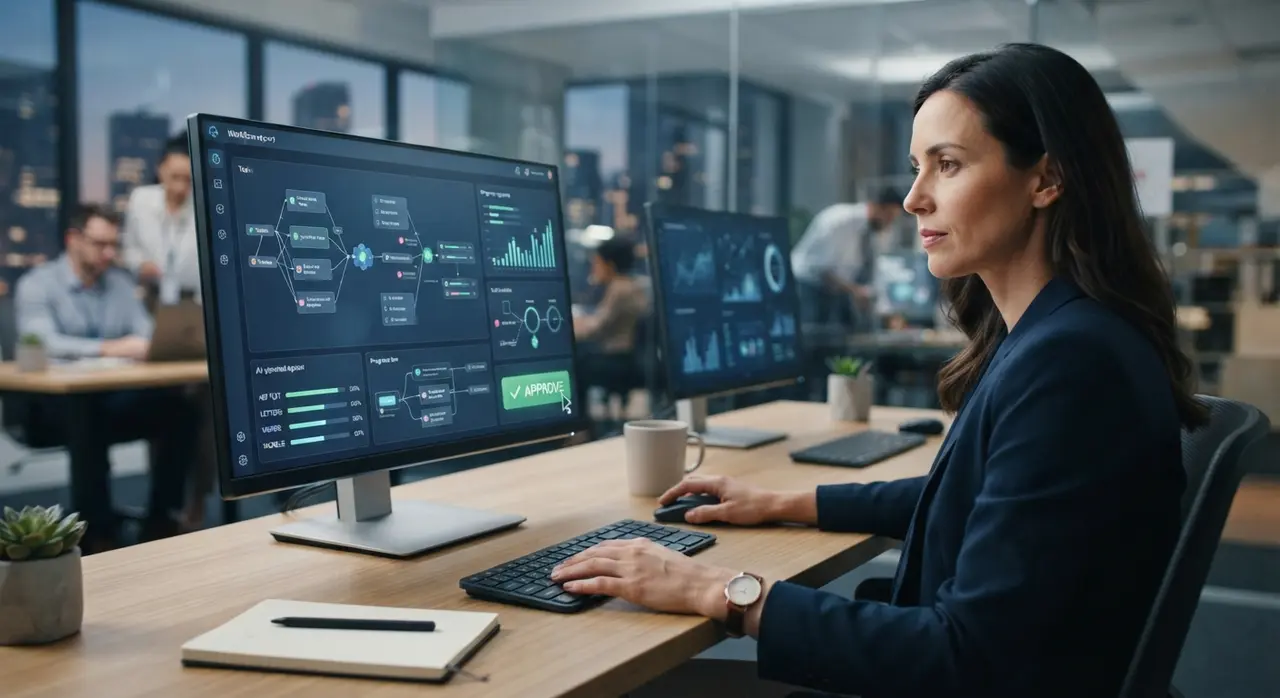
Automated output must always be subjected to human oversight before triggering operational actions or external communications. AI engines are exceptional at processing high volumes of unstructured data, but they lack contextual accountability.
Structuring human intervention points prevents automated mistakes from impacting core business operations. For example, in customer service or purchasing workflows, an agent can draft response letters or extract invoice fields, but a human manager must validate high-value exceptions.
Understanding the long-term benefits of AI automation relies on building systems where software handles repetitive computation while humans retain decision authority.
Connecting Policy Guidelines to Operational Systems (ERP, CRM, WhatsApp)
Policy enforcement must extend beyond written PDF guidelines directly into your daily operational software. A policy document lives on your internal wiki, but modern automated agents enforce guidelines programmatically through secure API layers.
When deploying enterprise agents, integration boundaries keep AI operations compliant with corporate standards:
- ERP Integration: Connecting AI agents integrated with SAP or Dynamics 365 ensures transactions adhere strictly to pre-set approval thresholds.
- CRM Synchronization: Restricting AI actions within Salesforce or Hubspot prevents unauthorized data modifications.
- WhatsApp Operations: Safeguarding automated customer service channels ensures AI agents never negotiate pricing or terms outside approved parameters.
Case Study: Enforcing Policy Governance in Multi-Branch Operations
A regional distributor managing logistics across multiple branch locations experienced inconsistent order entry and data leaks due to staff pasting customer manifests into public AI tools. To resolve this vulnerability, the executive leadership team engaged Agentes Autônomos to structure a enterprise-wide AI architecture.
Agentes Autônomos deployed localized enterprise AI agents integrated directly with their legacy ERP system while enforcing a strict operational policy. The results transformed their operations within 60 days:
- Zero customer PII exposed to public web LLMs.
- Order processing speeds increased by over 300% without expanding headcount.
- Human operators retained final approval authority for orders exceeding operational thresholds.
Implementation and Rollout: Training Teams without Smothering Innovation
Rolling out an enterprise AI policy requires ongoing education rather than punitive oversight. Employees typically turn to unsanctioned tools because they lack official, efficient alternatives for daily bottlenecks.
To successfully introduce your policy across all operating units:
- Appoint an AI Steering Committee: Combine leadership from IT, Legal, Operations, and HR.
- Provide Sanctioned Alternatives: Give teams access to private enterprise AI environments.
- Conduct Hands-On Training: Teach staff proper prompt engineering and verification techniques.
- Update Policy Quarterly: Revisit rules as technological capabilities and regulatory frameworks evolve.
Conclusion
A formal AI policy provides the foundation for safe, scalable enterprise automation. By establishing clear parameters around data privacy, tool selection, and human oversight, leadership can eliminate shadow AI risks while empowering teams to achieve peak productivity.
Frequently asked questions
What is a Generative AI Use Policy?
A Generative AI Use Policy is a formal enterprise document defining how employees may ethically and securely use artificial intelligence tools. It outlines permitted data inputs, approved platforms, and required review protocols for company tasks.
Why does every structured company need an AI policy?
Every structured company needs an AI policy to prevent intellectual property leaks, maintain regulatory compliance, and eliminate unverified AI errors. Without clear guidelines, informal use of public AI tools creates legal and operational exposure.
Can employees input customer data into public generative AI tools?
No, employees should never input non-public customer data or PII into standard public generative AI tools. Public models often retain input data for retraining, which violates data protection laws like LGPD and GDPR.
How often should a company update its AI governance policy?
A company should review and update its AI governance policy at least quarterly. Rapid advancements in model capabilities, integrations, and legal regulations require regular adjustments to keep guidelines effective and relevant.