Corporate AI Governance: Building Internal Agent Policies
Learn how to structure internal policies for corporate AI governance, define agent guardrails, enforce human-in-the-loop review, and safely scale AI.
- Corporate AI Governance
- Internal Policies
- AI Agents
- Enterprise Automation
- Risk Management
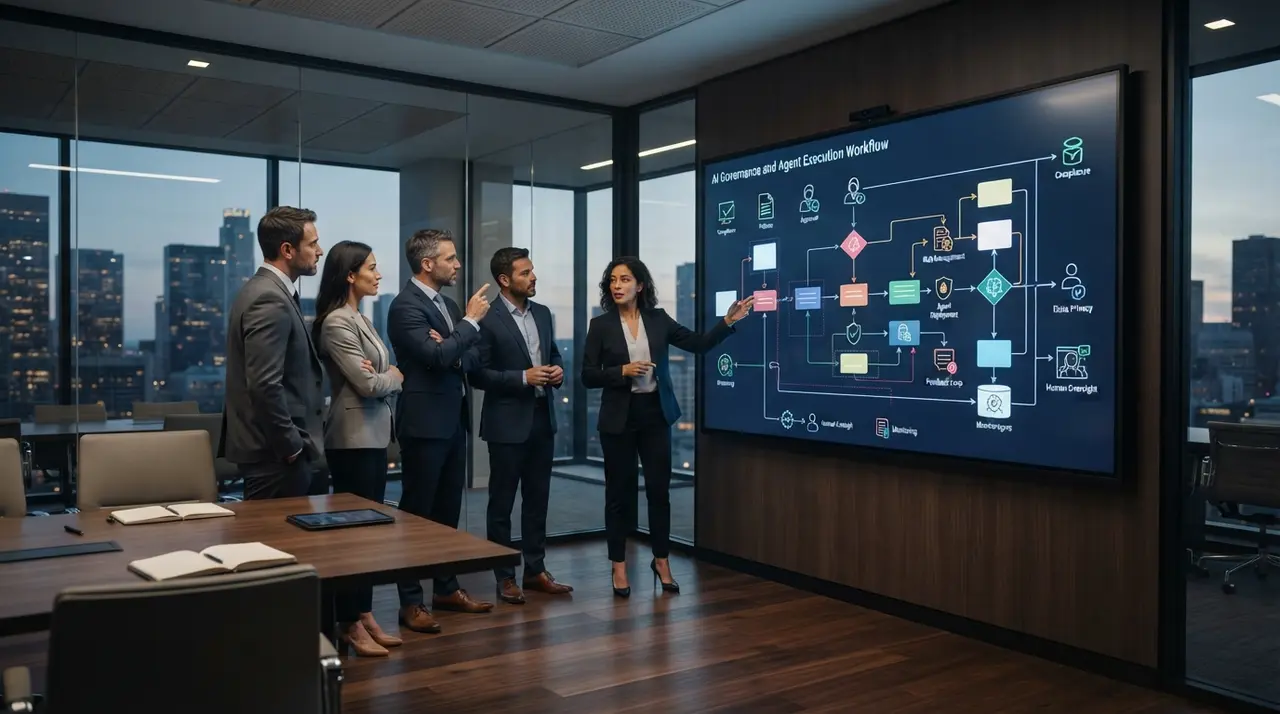
Corporate AI governance for autonomous software is the operational framework that establishes decision rights, liability, risk limits, and oversight for software executing business processes. Implementing structured internal policies allows enterprise leaders to automate high-volume tasks across ERP, CRM, and communication channels without compromising data security or operational compliance.
As organizations shift from basic generative chats to active workflow automation, the main challenge is no longer technology adoption—it is control. Without clear internal guardrails, scaling autonomous agents creates risks ranging from unauthorized system modifications to regulatory non-compliance. Establishing structured governance bridges the gap between rapid technological innovation and enterprise risk management.
Why Corporate AI Governance Is Essential for Enterprise Scale
Enterprise scale requires structured corporate AI governance to prevent compliance failures, operational bottlenecks, and unauthorized data exposure. When AI agents interact directly with legacy stack tools—such as SAP, Oracle, Microsoft Dynamics 365, or enterprise WhatsApp endpoints—they move from generating passive content to executing operational decisions.
Without a unified policy framework, departmental teams often deploy ad-hoc automations that operate outside standard IT and legal visibility. This shadow deployment leads to fragmented data access, unmonitored execution paths, and unclear accountability when an error occurs.
- Accountability Gaps: Defining whether the system vendor, IT team, or process owner is liable for an automated action.
- Data Leakage Risks: Preventing sensitive customer or financial data from escaping secure operational perimeters.
- Execution Errors: Preventing autonomous agents from misinterpreting edge cases in purchase orders, invoicing, or customer support ticketing.
By defining internal policies early, decision-makers can expand agentic AI capabilities across multi-unit operations while maintaining complete visibility over every automated transaction.
The Core Components of an Internal AI Governance Framework
A comprehensive corporate AI governance framework integrates committee oversight, clear process ownership, and continuous risk management controls. Governance should not act as a slow bureaucratic bottleneck; instead, it provides clear guidelines that enable business units to deploy autonomous workflows safely and independently.
| Framework Component | Focus Area | Responsible Role | Primary Key Metric |
|---|---|---|---|
| Executive Steering | Strategic alignment, risk appetite, policy approval | AI Steering Committee / C-Suite | Policy adoption rate & risk exposure |
| Process Ownership | Defining workflow scope, rules, and triggers | Department Heads / Operations Leads | Process execution accuracy (%) |
| Security & Compliance | Data privacy (LGPD/GDPR), access control, ISO 42001 | CISO / Legal & Compliance Team | Zero unauthorized data breaches |
| Technical Monitoring | API stability, runtime audit logs, exception handling | IT Infrastructure / DevOps Leads | System uptime & error recovery speed |
Establishing these four pillars ensures that every autonomous agent deployed in sales, finance, customer service, or logistics has a clearly designated owner and defined operating limits before reaching production environment.
Defining Guardrails, Action Limits, and Human-in-the-Loop Approval
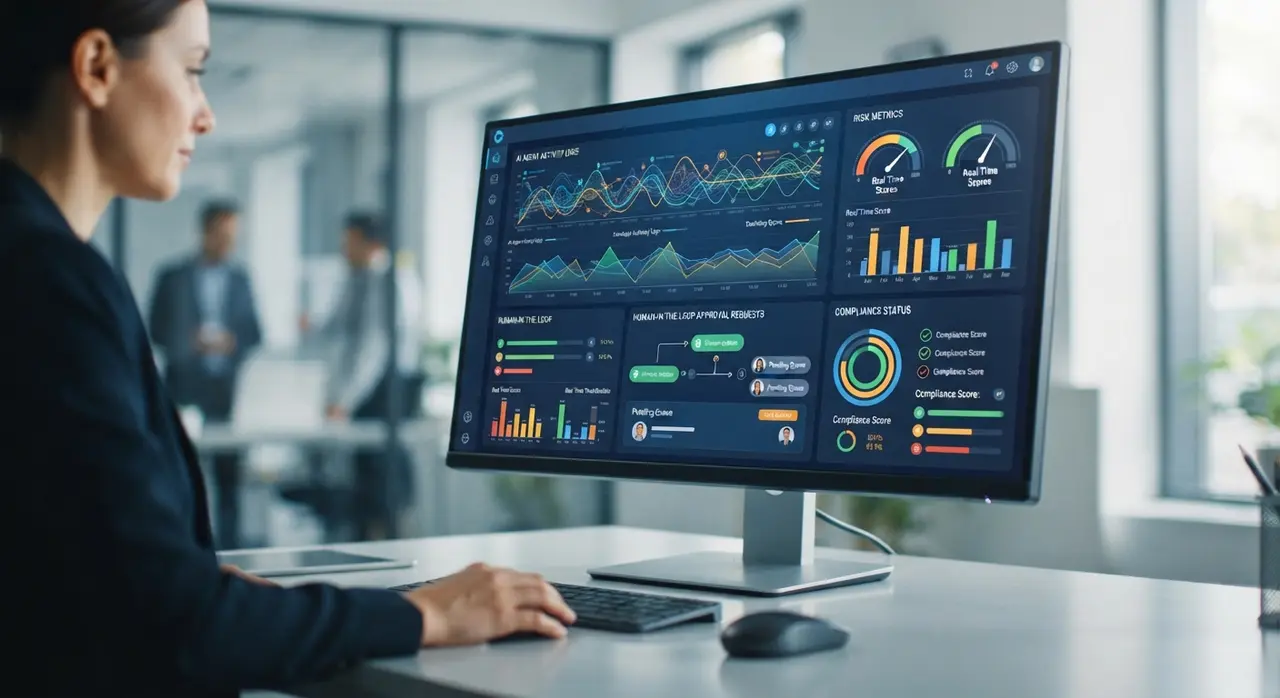
Guardrails determine the exact execution boundaries of autonomous software, ensuring that high-risk decisions require explicit human review before execution. Setting granular permission levels allows business units to maximize speed where risks are low while maintaining tight human control over critical decisions.
For instance, an AI agent handling procurement might automatically approve inventory orders under $1,000 based on ERP stock thresholds. However, if an order exceeds that amount or involves a new vendor, the agent drafts the transaction and routes an interactive approval request directly to the procurement manager via WhatsApp or CRM notification.
- Read-Only Operations: Extracting data from invoices, checking ERP stock levels, and compiling daily logistics summaries.
- Conditional Execution: Routing incoming customer support tickets or updating CRM deal stages according to strict rule triggers.
- Human-in-the-Loop Thresholds: Flagging high-value financial payouts, policy overrides, or contract signatures for mandatory human validation.
This hybrid oversight model preserves operational velocity while keeping full liability and final authority firmly in human hands.
Regulatory Alignment: ISO 42001 and Data Privacy Protocols
Aligning AI agent operations with standards like ISO 42001 and regulations such as LGPD ensures full auditability and lawful data processing across legacy systems. ISO 42001 provides the international standard for establishing, implementing, and continually improving an Artificial Intelligence Management System (AIMS).
When deploying agents across customer-facing or financial channels, companies must establish clear audit logs that record every prompt, response, system query, and human confirmation. Maintaining transparent record-keeping ensures that internal auditors and regulatory authorities can trace any execution back to its precise source trigger.
Key Governance Requirements for Enterprise Tools:
- Role-Based Access Control (RBAC): Ensure agents interact with ERP and CRM platforms using scoped service accounts that enforce least-privilege principles.
- Immutable Audit Trails: Store event logs for every automated transaction, including agent reasoning paths and human approvals.
- Vendor Security Diligence: Conduct rigorous vendor reviews using a structured AI agent vendor evaluation checklist before integrating third-party tools into operational workflows.
Case Study: Operational Governance in Multi-Unit Supply Chain Execution
Implementing structured governance enables enterprise operations to eliminate backlog and manual errors while maintaining full human oversight over financial thresholds. A multi-regional logistics company operating across eight fulfillment hubs integrated autonomous agents into their SAP ERP and WhatsApp driver communications to handle freight check-ins and invoice validation.
Before implementing governance, hub managers processed freight documentation manually, creating significant check-in delays and frequent input errors. Working with Agentes Autônomos, the organization defined a clear governance matrix: agents could process routine shipping slips and update stock records automatically, but any variance over 2% between purchase order and delivered weight triggered an automatic hold for human review.
- Operational Impact: Driver processing time decreased by 65% across all regional hubs.
- Error Reduction: Invoice matching discrepancies fell to near zero within the first 60 days.
- Governance Compliance: 100% of high-value discrepancies were successfully flagged and resolved by human process owners with complete audit records.
By embedding governance directly into daily operations, the company scaled automation across all units without modifying their existing ERP infrastructure or increasing administrative headcount.
Practical Steps to Implement Internal AI Policies Without Paralyzing Innovation
Balancing control and agility requires a phased implementation approach that begins with low-risk automated workflows before expanding into high-impact systems. Overly rigid policies created in isolation often drive employees to use unsanctioned tools, whereas flexible governance encourages safe experimentation within controlled environments.
Phase 1: Inventory and Risk Assessment
Map all current usage of AI tools across operations. Categorize workflows based on data sensitivity, financial impact, and client exposure to establish baseline risk levels.
Phase 2: Draft Actionable Guardrails
Establish plain-language internal guidelines detailing authorized use cases, mandatory human approval thresholds, and restricted data categories. Avoid vague directives by giving concrete examples for daily operational scenarios.
Phase 3: Deploy Automated Monitoring and Continuous Support
Integrate automated audit logging and monitor agent performance regularly. Establishing clear post-implementation AI support and monitoring ensures that policies adapt as underlying operational processes evolve.
Frequently Asked Questions
Frequently Asked Questions
What is corporate AI governance?
Corporate AI governance is the framework of policies, roles, risk assessments, and monitoring processes that guide how an enterprise develops and deploys artificial intelligence safely. It defines who is responsible for automated outcomes, sets security limits, and ensures compliance with internal guidelines and external regulations.
How do guardrails differ from traditional security policies?
Guardrails are dynamic, real-time boundaries programmed into autonomous workflows to limit what actions an AI agent can execute independently. While security policies state regulatory rules, guardrails actively enforce those rules by requiring human review or blocking actions that exceed predetermined threshold limits.
Does AI governance slow down business innovation?
Properly structured AI governance accelerates innovation by providing clear parameters within which teams can safely deploy automation. Rather than blocking projects, well-designed policies give department leads pre-approved frameworks to roll out new autonomous workflows without needing lengthy, case-by-case legal or IT approvals.
How should small and mid-sized enterprises start building AI policies?
Mid-sized enterprises should start simple by appointing an executive sponsor, creating an inventory of current AI use cases, and defining human-in-the-loop review thresholds for high-risk decisions. As operational maturity increases, companies can expand their policy framework into formal certifications like ISO 42001.