LGPD and AI Agents: Enterprise Compliance Checklist
Ensure complete LGPD compliance before deploying enterprise AI agents. Practical checklist covering data minimization, human review, and vendor contracts.
- LGPD compliance
- AI agents
- Data Privacy
- Enterprise AI
- Process Governance
LGPD and AI Agents compliance requires enterprises to establish valid legal bases, enforce strict data minimization, maintain human review for automated decisions, and secure robust controller-operator vendor contracts before deployment. Integrating autonomous agents into workflows that process personal data across CRM, ERP, and communication channels introduces structural legal, operational, and reputational risks under Brazil's General Data Protection Law (LGPD).
As organizations scale operational automation across sales, finance, customer support, and HR, autonomous agents frequently cross-reference data from multiple enterprise databases. Guaranteeing privacy compliance prior to go-live protects business leaders from severe legal penalties while ensuring seamless operational efficiency.
Valid Legal Bases for AI Agent Data Processing
Establishing an explicit legal basis under Article 7 of the LGPD is mandatory before any AI agent processes customer or employee data. Business leaders cannot rely on vague operational necessity; each autonomous workflow must map to a specific legal justification such as contract execution, legal obligation, or legitimate interest.
When deploying agents to query enterprise systems like CRM platforms or WhatsApp channels, identifying the exact processing scope prevents regulatory violations. For example, processing customer phone numbers to send order updates falls cleanly under contract execution, whereas using behavioral history to generate proactive upsell prompts requires evaluating legitimate interest alongside data subject rights.
- Execution of Contract: Applied when agents handle direct operational tasks requested by the data subject, such as processing returns or scheduling service visits.
- Legitimate Interest: Requires a formal Legitimate Interest Assessment (LIA) to balance business gain against individual privacy rights.
- Consent: Necessary when agents process sensitive personal data or perform secondary marketing profiling not directly tied to core service delivery.
Data Minimization and Privacy by Design in Agent Architecture
AI agents must be architected to collect, transmit, and retain only the minimum data attributes strictly necessary to execute their assigned task. Excessive data exposure to Large Language Models (LLMs) increases security vulnerabilities and breaches LGPD principles.
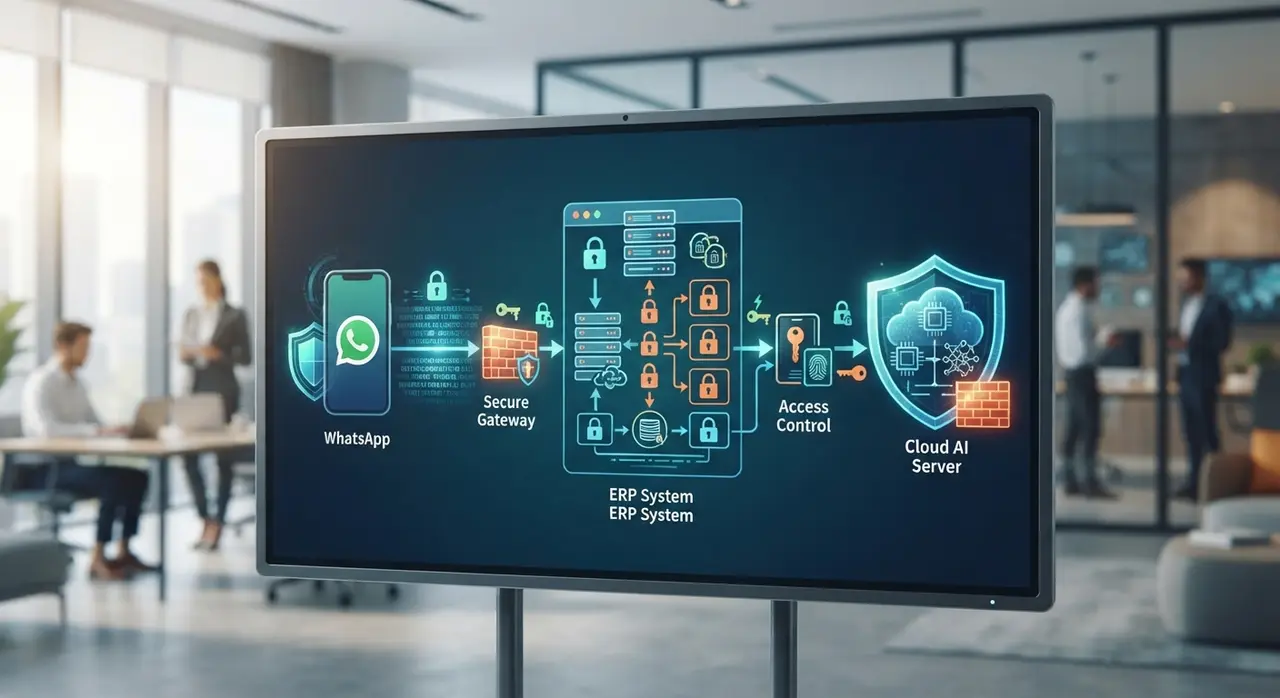
Implementing technical safeguards like real-time data masking ensures sensitive fields—such as tax IDs (CPF), financial balances, or health details—are redacted before prompts reach third-party processing endpoints. Combining contextual data filtering with robust access controls limits agent visibility strictly to relevant tables within your enterprise stack.
By prioritizing privacy by design, companies prevent unauthorized data leaks across internal departments and multi-unit operations while maintaining auditability.
Automated Decision-Making and the Right to Human Review
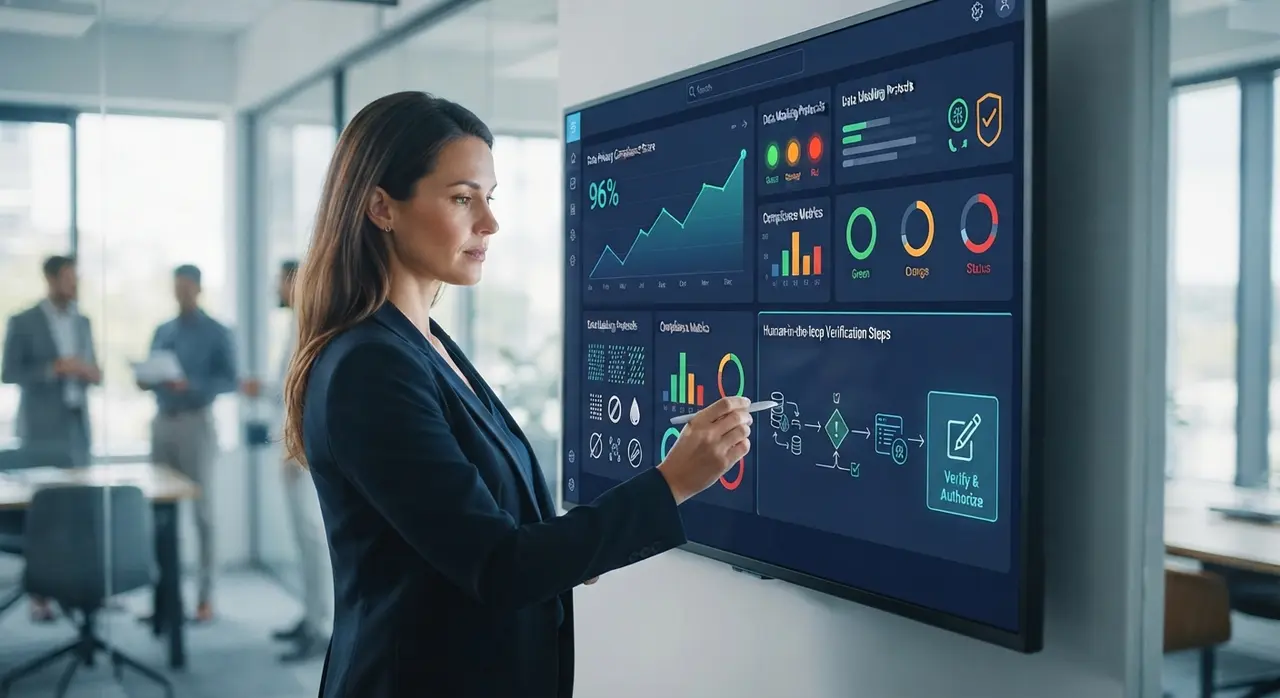
Article 20 of the LGPD grants data subjects the right to request human review and clear explanations for decisions made solely by automated systems. When autonomous agents evaluate credit limits, approve supplier invoices, or screen job applicants, business leaders must implement transparent audit trails and human-in-the-loop (HITL) overrides.
Relying completely on autonomous outputs for high-impact decisions exposes organizations to legal challenges if an agent denies a transaction without explainable criteria. Designing fallback mechanisms ensures complex or flagged cases automatically route to human supervisors before final execution.
To learn more about structuring enterprise governance for operational workflows, explore our detailed guide on agentic AI enterprise governance.
Controller vs. Operator Dynamics in AI Vendor Contracts
Enterprise contracts with AI software providers must explicitly clarify whether the vendor acts as a data controller or data operator under LGPD guidelines. In most agent deployments, your company remains the data controller determining processing purposes, while the AI solution vendor acts strictly as an operator.
Contractual agreements must prohibit vendor partners from using your proprietary customer or operational data to train their public foundation models. Additionally, cross-border API calls to international cloud infrastructure demand strict compliance with LGPD international data transfer provisions.
- Data Processing Agreements (DPA): Bind vendors to process data strictly according to documented controller instructions.
- Model Training Restrictions: Mandate zero-data-retention (ZDR) clauses to ensure inputs and outputs are not retained for LLM retraining.
- International Transfers: Verify that cloud infrastructure providers maintain standard contractual clauses (SCCs) compliant with Brazilian law.
For additional criteria when evaluating software partners, refer to our comprehensive AI vendor evaluation checklist.
Practical Pre-Implementation LGPD Checklist
Every business must guarantee that operational readiness audits are conducted across technical, legal, and operational vectors prior to launching autonomous agents. The following structured framework outlines mandatory validation steps before moving agents into production environments.
| Checklist Category | LGPD Requirement | Technical & Operational Action | Responsible Lead |
|---|---|---|---|
| Legal Grounding | Article 7 Compliance | Document legal bases for every dataset accessed by the agent across ERP and CRM. | Legal & DPO |
| Data Minimization | Article 6 (III) | Implement prompt filtering and automated PII masking before API transmission. | Engineering & Security |
| Explainability | Article 20 | Log decision parameters and build one-click human escalation in WhatsApp/ERP. | Operations Lead |
| Vendor Due Diligence | Articles 39 & 40 | Execute DPAs with ZDR clauses and verify international transfer standard terms. | Procurement & IT |
| Incident Management | Article 48 | Establish automated alert protocols for unauthorized data access attempts. | CISO & Operations |
Real-World Case: Compliance-First Automation at Agentes Autônomos
A multi-unit commercial distribution firm partnered with Agentes Autônomos to automate order status verification and invoice resolution across WhatsApp and enterprise ERP systems. The organization needed to process over 15,000 monthly customer inquiries without exposing confidential buyer tax IDs or credit profiles to public cloud endpoints.
Agentes Autônomos integrated custom enterprise AI agent solutions equipped with an inline data-scrubbing middleware layer. This architecture stripped PII prior to agent reasoning, enforced strict HITL routing for credit boundary exceptions, and maintained fully searchable audit logs accessible to the company’s Data Protection Officer (DPO).
As a result, the enterprise reduced customer response times by 70% while achieving 100% compliance during internal regulatory audits, proving that stringent compliance and high-speed automation coexist seamlessly.
Frequently asked questions
Does LGPD prohibit using customer data in AI agents?
No, LGPD does not prohibit using customer data in AI agents, provided the organization establishes a legal basis under Article 7 and enforces data minimization. Companies must ensure personal data processing is transparent, secure, and limited strictly to defined operational goals.
What happens under LGPD if an AI agent makes a mistake in an automated decision?
Data subjects have the right to request human review and an explanation of any decision made solely by automated processing under Article 20 of the LGPD. Organizations must implement human-in-the-loop workflows to review, modify, or override automated agent outcomes upon request.
Can vendors use our enterprise data to train their public AI models?
Enterprise data should never be used to train public models unless explicit consent or contractual authorization is granted. Companies must ensure Data Processing Agreements (DPAs) with AI vendors include zero-data-retention clauses that restrict models from retaining proprietary inputs.
What is the first step every enterprise must guarantee before deploying AI agents?
The first step is conducting a complete data mapping audit to identify what personal data the agent will access, process, and store across CRM, ERP, and chat platforms. This audit ensures legal bases are documented and data masking filters are applied prior to go-live.