CISO and Compliance Role in Enterprise AI Governance
Learn how engaging the CISO and compliance early ensures secure enterprise AI adoption, mitigates prompt risks, protects data, and maintains LGPD compliance.
- CISO
- Compliance
- AI Governance
- Enterprise Security
- AI Agents
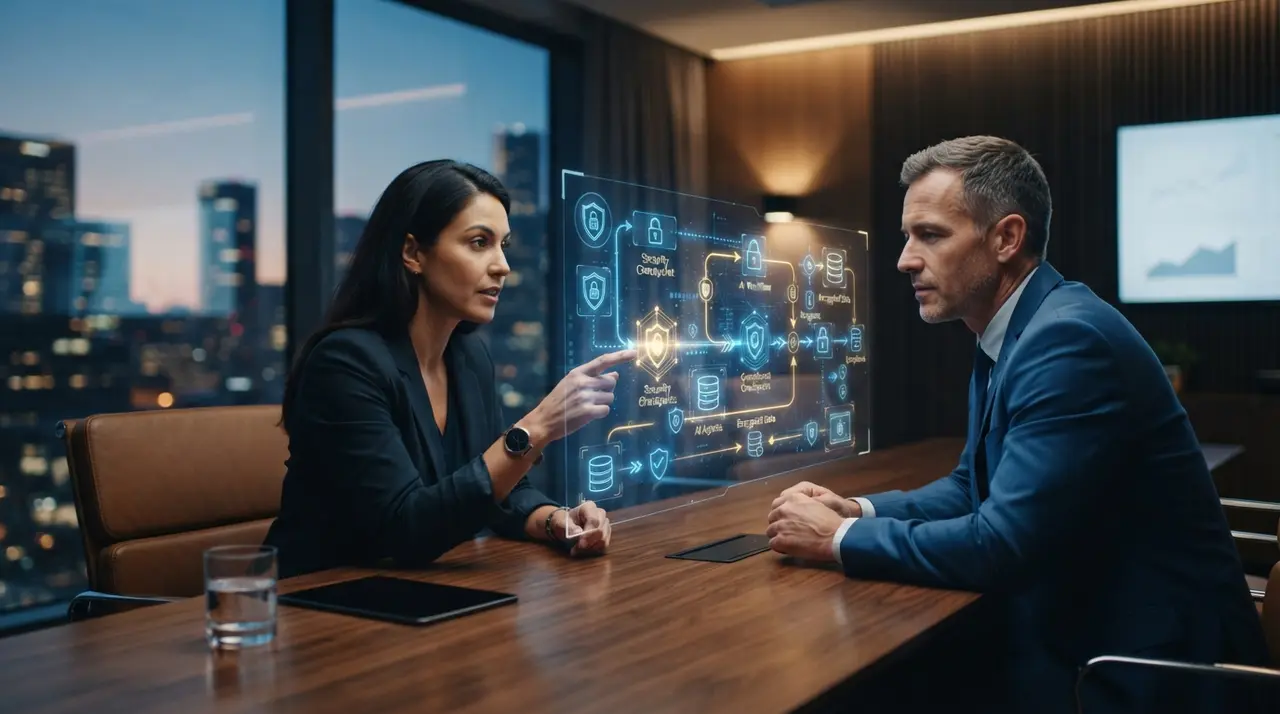
The role of the CISO and the compliance area in corporate AI adoption is to establish security and governance frameworks that prevent data leaks, unauthorized access, and regulatory penalties. Involving chief information security officers and compliance leads from the start guarantees that AI agents operate safely within existing enterprise workflows without halting operational innovation.
As companies move from simple chatbots to autonomous operational agents connected directly to ERPs, CRMs, and customer communication channels, the risk perimeter expands. Unchecked autonomous execution can lead to unintended financial transactions, data exposure, and compliance violations if security controls are treated as an afterthought.
Why Early CISO and Compliance Involvement Prevents Rework
Early collaboration between executive leadership, CISO, and compliance teams prevents costly infrastructure redesigns and post-deployment security breaches. When technical architectures are built without security input, organizations often face project freezes right before launch due to unmitigated data privacy and access control risks.
Enterprise AI agents process sensitive operational data, evaluate business logic, and execute multi-step actions across internal software systems. Integrating security and governance during the initial design phase ensures that API access, data masking, and user permissions are embedded naturally into the workflow.
Key benefits of early security alignment include:
- Preventing Architectural Refactoring: Avoid rebuilding custom integrations to satisfy security protocols after deployment.
- Ensuring Regulatory Alignment: Guarantee continuous adherence to data privacy laws like LGPD and GDPR before handling production data.
- Defining Scope Limits: Establish precise boundaries for what an autonomous agent can read, write, or execute.
- Accelerating Time-to-Value: Eliminate late-stage security audits that delay operational rollout across business units.
Core Security Concerns: Data Access, Prompt Injection, and Leakage
Enterprise AI agents create expanded attack surfaces that require robust access controls, prompt injection defenses, and strict data leakage prevention mechanisms. Because agents process context dynamically, standard web application firewalls alone cannot protect against context manipulation or data exfiltration.
Chief Information Security Officers (CISOs) must evaluate how agents interact with internal databases and external APIs. If an agent is granted elevated database credentials without role-based access control (RBAC), an attacker could exploit input fields to force the agent into revealing restricted executive records or payroll data.
Evaluating system safeguards requires checking solutions against a structured vendor evaluation checklist before deploying agents into sensitive corporate networks.
Major security risks unique to autonomous AI agents include:
- Direct and Indirect Prompt Injection: Malicious inputs embedded in incoming customer emails, WhatsApp messages, or web forms that manipulate the agent's core instructions.
- Data Leakage via Context Windows: Sensitive customer or corporate data leaked to unauthorized users through poorly scoped prompt context.
- Unauthorized API Action Execution: Agents performing destructive write actions—such as approving unauthorized discounts or updating master supplier tables—due to weak authorization boundaries.
- Unsecured Third-Party Integrations: Vulnerabilities introduced when connecting autonomous workflows to external vendor APIs without zero-trust validation.
Compliance Requirements: Data Privacy, Auditability, and Sectoral Rules
Compliance oversight ensures that automated decisions remain fully audit-ready and aligned with global privacy standards such as LGPD and GDPR. In regulated sectors like finance, healthcare, and retail, automated systems must provide complete transparency regarding how inputs yield specific operational outputs.
The compliance team must verify that data retention policies, consent frameworks, and anonymization procedures are respected throughout the lifecycle of the AI model. If an automated workflow updates customer accounts or modifies billing schedules, every single step must leave an immutable audit record.
Understanding advanced agentic AI capabilities allows compliance leaders to design monitoring frameworks tailored specifically to multi-step reasoning systems.
| Governance Dimension | Traditional Software | Generative Chatbots | Autonomous AI Agents |
|---|---|---|---|
| Access Scope | Static permissions per user ID | Read-only interface for documentation | Dynamic API execution across CRM, ERP, and databases |
| Primary Security Risk | Code vulnerabilities and credential leak | Hallucinations and informal data leak | Prompt injection, unauthorized action execution, and privilege escalation |
| Compliance Obligation | System availability and access logs | Content filtering and basic data privacy | Full decision auditability, human-in-the-loop logs, and strict LGPD alignment |
| Control Mechanism | Fixed business logic and user roles | System prompts and output moderation | Structured guardrails, fallback thresholds, and RBAC sandboxing |
Building Guardrails: Human-in-the-Loop and Audit Logs
Operational guardrails protect enterprises by combining real-time execution logs with mandatory human approval for critical financial or operational decisions. Establishing systematic boundaries ensures that high-risk edge cases are automatically routed to human managers before execution occurs.
A well-architected guardrail framework categorizes actions by operational impact. Low-risk tasks—such as sending order status updates or categorizing incoming support tickets—run fully automatically. Medium to high-risk operations—such as issuing refunds, altering credit limits, or updating supplier contracts—require explicit human sign-off.
Key elements of enterprise AI guardrails:
- Confidence Threshold Triggers: Automatically escalate transactions to human supervisors whenever the agent's confidence score drops below defined limits.
- Financial Spending Controls: Set strict monetary limits per transaction and per day for automated purchasing or settlement workflows.
- Immutable System Logs: Record input prompts, system responses, context data, and API payloads in centralized, write-once log repositories.
- Real-Time Anomaly Detection: Monitor execution frequency and volume spikes to catch infinite loops or compromised input patterns immediately.
Governance Frameworks: Applying ISO 42001 and Policy Standards
Standardized AI governance frameworks like ISO 42001 provide structured guidelines for continuous risk assessment, policy creation, and system monitoring. Implementing recognized standards gives executive boards and audit committees confidence that corporate AI deployments follow international best practices.
ISO/IEC 42001 specifies the requirements for establishing, implementing, maintaining, and continually improving an Artificial Intelligence Management System (AIMS). It equips CISOs and compliance teams with a systematic method to manage AI-specific risks, such as algorithmic bias, system drift, and unexpected operational failures.
Consider how modern enterprises implement these controls in practice:
Mini-Case: Multi-Unit Logistics & Retail Operations
A national distribution group with over 40 units integrated custom AI agents into their legacy ERP and WhatsApp customer channels to process order changes and inventory allocations. By partnering with Agentes Autônomos to implement tailored tailored AI agent solutions, the company instituted robust RBAC controls, automated PII scrubbing, and mandatory human review for order adjustments exceeding $5,000. As a result, the firm reduced customer service queue resolution times by 70% while maintaining zero compliance breaches and full LGPD alignment.
Balancing Innovation and Governance Without Halting Execution
Organizations balance speed and control by establishing tiered authorization levels for AI agents rather than imposing blanket operational bans. A rigid security stance that blocks all AI adoption leads to shadow AI, where business units independently adopt unvetted consumer tools without IT knowledge.
CISOs and compliance heads should act as enablers of secure innovation by creating standard operating procedures (SOPs) and pre-approved deployment pipelines. By defining clear sandbox environments, testing methodologies, and access protocols, companies can rapidly prototype and scale AI agents safely.
To maintain balance between speed and control:
- Create a centralized cross-functional AI governance board (CISO, Legal, Operations, and Business Unit Leads).
- Maintain an active inventory of all deployed agents, API connections, and data access levels.
- Run periodic penetration tests and prompt injection simulations against deployed agents.
- Offer internal guidelines on safe AI usage to foster a security-first culture across operational teams.
Frequently asked questions
What is the role of the CISO in corporate AI agent adoption?
The CISO is responsible for assessing security risks, defining data access boundaries, preventing prompt injection attacks, and ensuring secure API integrations with existing corporate tools. They establish the technical defense framework that keeps corporate systems safe while autonomous agents execute operational tasks.
How does the compliance team ensure AI agents adhere to LGPD and GDPR?
Compliance teams audit data handling practices, implement data minimization principles, restrict personally identifiable information (PII) usage in context windows, and enforce immutable decision logs. They ensure that all automated processes comply with privacy laws and sector-specific regulatory standards.
What are the primary security risks of deploying autonomous AI agents?
The primary security risks include prompt injection attacks, sensitive data leakage through prompt context, unauthorized API execution, and privilege escalation within linked ERP or CRM systems. Without proper guardrails, agents can inadvertently alter corporate data or expose confidential records.
How can companies control high-risk decisions made by AI agents?
Companies implement human-in-the-loop (HITL) workflows, dynamic confidence threshold triggers, and predefined financial authorization limits. When an agent encounters high-value or ambiguous transactions, the task is automatically flagged and routed to a human supervisor for manual approval.